
Cybersecurity in the UK has reached a critical juncture, with 43% of businesses experiencing cyber breaches or attacks in the past year.
Recent high-profile incidents highlight the urgent need for solid defences, including the devastating attack on Marks & Spencer in April 2025, which cost the retailer approximately £300 million and forced them to suspend online operations for months. The attack, attributed to the criminal group “Scattered Spider,” showed how even established businesses can fall victim to sophisticated threats.
Step 1: Carry Out a Thorough Cyber Risk Assessment
The foundation of effective cybersecurity is in understanding your vulnerabilities through a thorough risk assessment. This approach starts with defining the scope of your assessment, cataloguing critical assets and systematically evaluating threats and vulnerabilities that could impact your organisation.
Begin by identifying and prioritising your most valuable digital assets, including customer data, intellectual property, financial systems and operational technology. Map how these assets interconnect and determine which systems are essential for business continuity. Evaluate potential threats by considering both external actors, such as cybercriminal groups and internal risks from employees or contractors with system access.
Rate risks according to their potential impact and likelihood of occurrence. Government guidance indicates that only 29% of businesses conducted cyber risk assessments in 2024, despite the clear benefits of proactive risk management. High-impact, high-likelihood scenarios should receive immediate attention, whilst lower-probability threats can be addressed through longer-term strategic planning. Document your findings and establish regular review cycles to guarantee that risk assessments remain current.
Step 2: Establish a Secure Technical Baseline
Implementation of good technical defences is the basis of effective cybersecurity. The National Cyber Security Centre’s “10 Steps” framework guides the establishment of security foundations that protect against common attacks.
Deploy strong perimeter defences, including firewalls, intrusion detection systems, and secure network architecture. Implement rigorous patch management processes to make sure all software and systems receive timely security updates, as unpatched vulnerabilities remain primary attack vectors for cybercriminals.
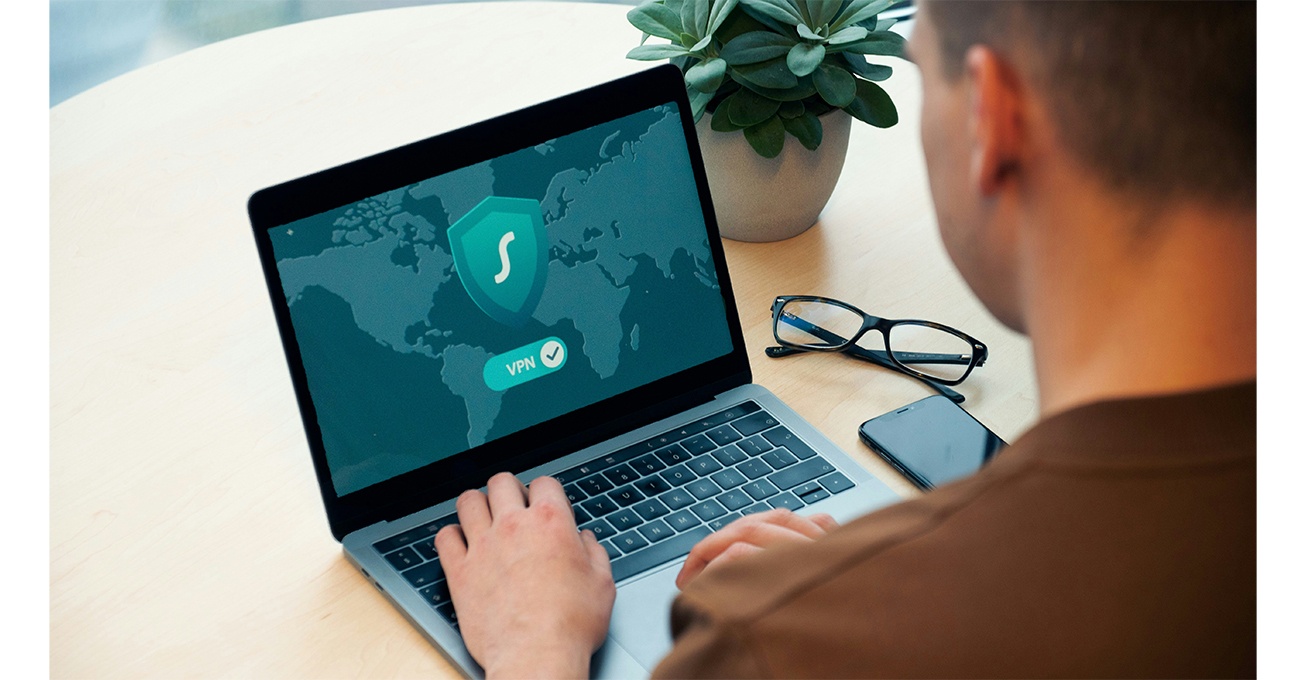
Multi-factor authentication should be mandatory for all system access, providing additional security layers even when credentials are compromised. Using a reliable VPN for business guarantees encrypted remote access for employees working off-site, protecting sensitive communications from interception.
Deploy endpoint protection across all devices connecting to your network, including company-owned laptops, mobile devices, and any approved personal equipment used for business purposes. Regular security monitoring and logging provide visibility into network activity and help identify potential threats before they cause significant damage.
Step 3: Strengthen Governance and Training
Effective cybersecurity needs strong governance structures and well-trained personnel who understand their roles in maintaining security. Company directors must actively engage with cyber governance, ensuring adequate resources are allocated and security considerations are integrated into strategic decision-making processes.
Training programmes should cover recognising phishing attempts, secure password practices, safe handling of sensitive information and proper procedures for reporting suspicious activities. Establish clear incident response procedures that define roles and responsibilities when security incidents occur. These procedures should include communication protocols, escalation paths, and recovery processes that minimise business disruption.
Cyber governance should include regular board-level reporting on security posture, threat landscape developments and investment requirements. This executive oversight guarantees that cybersecurity receives appropriate attention and resources while maintaining alignment with broader business objectives and risk appetite.
Strengthening cybersecurity needs sustained commitment across technological, procedural, and human dimensions. Organisations that invest comprehensively in risk assessment, technical controls, and governance frameworks position themselves to withstand new threats whilst maintaining operational resilience and customer trust in a challenging digital environment.